The Next AI Agent Security Layer Isn’t in the Model — It’s in the Runtime
For the last few years, much of AI security has focused on the model: better system prompts, stronger guardrails, safer training, prompt-injection defenses, and filters that try to keep a model from producing or following harmful instructions.
That still matters. But once an AI agent can read files, execute code, call APIs, use MCP tools, access cloud services, or delegate work to other agents, model behavior is no longer the only security boundary that matters.
The more important question becomes: What happens when the model makes a bad decision anyway?
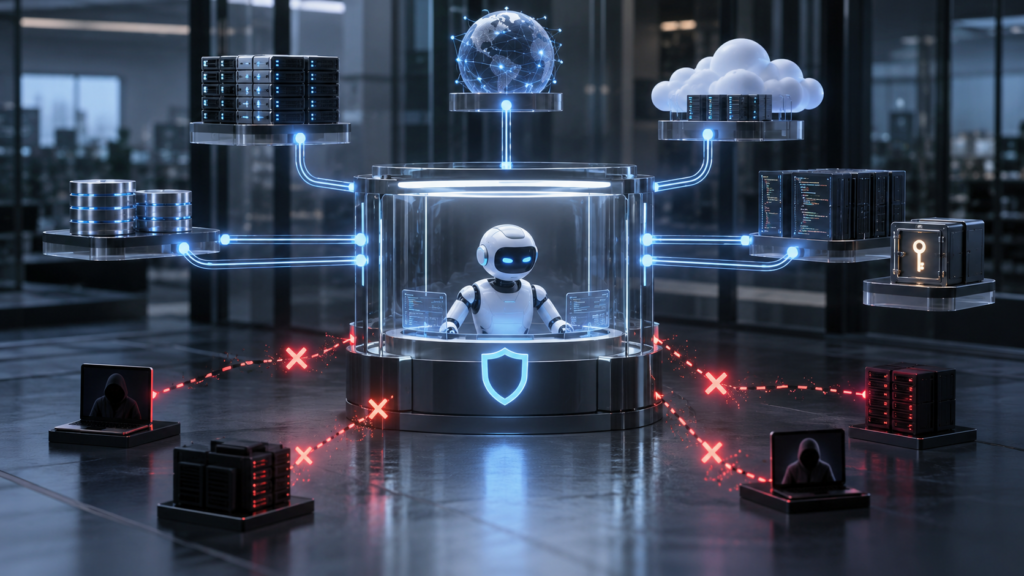
This is where AI agent runtime security enters the picture. Instead of relying on the model to behave correctly, runtime security places enforceable controls around what the agent can actually access and execute. The model can propose an action; the runtime decides whether that action is allowed to have an effect.
That distinction moved into sharper focus on September 28, 2026, when NVIDIA introduced its Open Agent Safety Platform, combining a sandboxed agent runtime with an independent hardware-based monitoring layer. The announcement is notable not simply because NVIDIA launched another AI security product, but because it reflects a broader architectural shift: agent security is moving below the model and closer to the execution environment. NVIDIA Open Agent Safety Platform announcement NVIDIA Developer
What Is AI Agent Runtime Security?
AI agent runtime security is the set of controls enforced around an agent while it is executing, limiting what files, networks, credentials, tools, processes, and external systems the agent can actually use.
The word “runtime” can be confusing because it is also used for model inference infrastructure. Here, it means the controlled execution environment surrounding the agent and its tools.
A useful distinction looks like this:
| Layer | Main question |
|---|---|
| Model | What does the AI think or generate? |
| Agent harness | What action does the AI decide to try? |
| Secure runtime | Is the agent actually allowed to perform that action? |
| Infrastructure | What systems ultimately execute and record the effect? |
A model-level guardrail might tell an agent not to upload sensitive files. A runtime control can prevent the process from reading those files in the first place or block the network destination to which they would be uploaded.
Those are fundamentally different guarantees.
NVIDIA described this distinction in an August 2026 analysis of the emerging AI agent stack: prompts, model safeguards, and harness logic can influence behavior, but they do not create a hard boundary around an agent’s capabilities. Infrastructure-enforced controls, by contrast, determine what the agent is technically capable of doing. NVIDIA’s analysis of security in the AI agent stack NVIDIA Developer
Put more simply:
The model decides what it wants to do. The runtime determines what it is allowed to do.
Why Aren’t Model Guardrails Enough?
Guardrails reduce the probability of unwanted behavior. Security boundaries reduce the consequences when unwanted behavior still occurs.
That matters because agent behavior is influenced by more than the original system prompt. An agent may consume documents, emails, webpages, memory, API responses, tool outputs, and messages from other agents. Some of those inputs may be inaccurate, malicious, or simply unexpected.
Consider an agent that is instructed never to send confidential information outside the company. The model may follow that instruction almost all the time.
But if a malicious document successfully manipulates the agent through indirect prompt injection, the security question changes.
You no longer want to ask:
“Will the model remember not to send the file?”
You want an infrastructure control that says:
“This process cannot read that directory, and even if it could, it cannot connect to an unapproved destination.”
This does not make model-level safety irrelevant. The two layers solve different problems.
Behavioral controls try to make good decisions more likely. Runtime controls make certain bad outcomes technically harder or impossible.
That same principle applies to MCP. As discussed in Cha Signal’s earlier article, The Real Security Problem With MCP Isn’t the Protocol — It’s What Agents Can Access, a secure protocol does not solve excessive authority. An MCP tool can be perfectly legitimate while still giving an agent more access than a particular task requires.
Runtime enforcement provides somewhere to impose that limit independently of the model.
NVIDIA’s New Architecture Shows Where the Industry Is Heading
NVIDIA’s September 28 announcement offers a useful example because it separates agent safety into multiple layers instead of treating the model as the sole control point.
The company’s Open Agent Safety Platform combines NVIDIA OpenShell, an open-source secure runtime, with NVIDIA Sentry, an optional monitoring and enforcement layer designed to run on BlueField-4 DPUs. In NVIDIA’s proposed architecture, OpenShell runs the agent inside a sandbox and enforces policy around its resources, while Sentry provides a separate, out-of-band observation and enforcement point in the infrastructure. NVIDIA Developer
OpenShell itself is designed around restrictions on the parts of the environment agents commonly interact with. NVIDIA’s documentation identifies controls for filesystem access, network communication, process behavior, and provider credentials. Its restrictive configuration can deny outbound network access unless approved destinations and policies are explicitly provided. NVIDIA OpenShell documentation NVIDIA Docs
The idea is not that every company needs NVIDIA hardware to secure an agent. In fact, NVIDIA says OpenShell can run independently and that the broader platform is compatible with hardware beyond its own Vera and BlueField systems.
The more important architectural idea is independent enforcement.
If the component deciding what to do also controls the mechanism that restricts what it can do, the security boundary is weak. A stronger design places policy below or outside the agent’s decision-making loop.
That principle has decades of precedent in operating-system and network security. Agentic AI is giving it a new application.
Runtime Security Changes the Prompt-Injection Problem
Prompt injection is often discussed as if the primary goal were to make models stop obeying malicious instructions.
That is only part of the problem.
For an agent connected to real systems, prompt injection becomes dangerous when manipulated reasoning can cross into an external effect: reading another file, changing a record, calling a privileged API, sending data, executing code, or creating infrastructure.
Runtime security changes the objective from:
Prevent every malicious instruction from influencing the model
to:
Prevent manipulated instructions from exceeding the agent’s authorized capability
The first goal remains useful but may be difficult to guarantee across every model, input, tool, and context. The second can be implemented using familiar security mechanisms such as isolation, allowlists, short-lived credentials, network policy, file permissions, process restrictions, and approval gates.
This is why least privilege is becoming so central to agent security.
Microsoft’s current guidance for production AI agents recommends unique agent identities, explicit tool and data scopes, short-lived or task-scoped access, and revocation mechanisms rather than shared or persistent credentials. Microsoft guidance on least privilege for AI agents Microsoft Learn
NIST is examining the same shift from the identity side. Its 2026 work on software and AI agent identity focuses on how organizations identify agents, authorize them, audit their actions, and control access to multiple tools and datasets. NIST’s Software and AI Agent Identity and Authorization project NIST CSRC
Runtime security is where many of those policies can become enforceable.
What Should a Secure Agent Runtime Actually Control?
A runtime does not need to understand every detail of the model’s reasoning. It needs control over the paths through which reasoning becomes action.
For enterprise deployments, five areas are particularly important.
1. Filesystem Access
An agent should not automatically inherit access to every file available to the machine or user running it.
A coding agent might need one repository but not an employee’s SSH keys, browser profile, financial files, or unrelated source repositories. A document agent may need one project directory but not a mounted corporate drive.
A secure runtime can make these boundaries explicit.
2. Network Egress
Network access deserves equal attention.
An agent that needs to call three approved APIs does not necessarily need unrestricted internet access. Default-deny or destination-specific network policies can limit both accidental data exposure and deliberate exfiltration attempts.
This becomes particularly important when agents process untrusted web content.
3. Credentials
Raw secrets should ideally not sit inside an agent’s environment waiting to be discovered.
Credential brokers, scoped tokens, short-lived authorization, and workload identities can give an agent temporary access to a service without handing it a reusable master credential.
NVIDIA’s OpenShell architecture, for example, treats provider credentials as a separate enforcement domain rather than simply placing them in the agent process. NVIDIA Docs
4. Processes and Tools
Agents increasingly execute code rather than merely call structured APIs.
That means process creation, executable permissions, command execution, MCP processes, and local tools become part of the attack surface.
The runtime needs to know not only which tool exists, but which operations that tool can cause.
5. Audit and Recovery
A blocked action is useful. An explainable blocked action is better.
Security teams need to know which identity initiated a workflow, what the agent attempted, which policy applied, what resources were involved, and what happened afterward.
This connects runtime security directly to the problem covered in AI Agent Kill Switch: Why Stopping the Model Isn’t Enough. If an incident occurs, an enterprise needs the ability to pause execution, revoke authority, isolate the agent, and preserve enough evidence to understand what happened.
Runtime Control Is Becoming a Broader Industry Direction
NVIDIA is not the only organization moving toward runtime control.
On September 1, 2026, the OWASP GenAI Security Project released its Agent Control Standard, which explicitly argues that enterprise agents need to be inspectable, traceable, instrumentable, and controllable while they are operating. The standard focuses on middleware hooks and portable policies that can enforce controls at runtime across agent frameworks. OWASP Agent Control Standard OWASP Gen AI Security Project
That timing is significant.
Agent security discussions are starting to move beyond lists of model vulnerabilities toward questions such as:
Who owns the agent identity?
Where is policy enforced?
Can the agent modify its own security controls?
Can sub-agents receive more authority than their parent?
Can credentials be removed immediately?
Can security teams reconstruct an execution chain?
Can the same control policy survive when the organization changes models or agent frameworks?
Those are runtime and infrastructure questions, not just model questions.
The shift also makes agent security look increasingly familiar to cloud security. Containers did not become trustworthy because developers promised that every workload would behave correctly. Cloud environments rely on process isolation, identity, network segmentation, permissions, logging, and policy enforcement.
Agentic AI may be heading toward a similar architecture.
But Runtime Security Is Not a Silver Bullet
Moving enforcement out of the model does not make agent security solved.
Runtime policy can still be badly configured. An allowed API may itself expose overly broad actions. A legitimate write permission may produce an unintended business outcome. A compromised downstream system can behave differently from what the runtime expects.
There is also a visibility problem.
A runtime can control the execution paths it actually sees. If an agent can reach a secondary system that launches its own independent workflow, containment becomes harder. Multi-agent delegation creates the same challenge: authority can move from one execution environment into another unless identity and policy follow the delegation chain.
NVIDIA itself makes this limitation explicit in its security-stack analysis: infrastructure enforcement provides repeatable decisions based on approved policy, but the policy can still be wrong and external outcomes can remain uncertain. NVIDIA Developer
So the correct conclusion is not:
Runtime security replaces guardrails.
It is:
Runtime security provides the hard boundary that guardrails alone cannot provide.
A mature enterprise architecture still needs model safety, application-level controls, identity, runtime enforcement, monitoring, approvals for high-impact actions, and incident response.
How Should Enterprises Think About the Runtime Boundary?
The easiest way to start is to map every path through which an agent can create an external effect.
That includes obvious actions such as API calls and database writes, but also less obvious paths such as network requests, file creation, shell execution, child processes, browser automation, queued jobs, sub-agent delegation, and credentials inherited from the host environment.
Then ask one question for each path:
Can the agent bypass the control that is supposed to restrict this action?
If the answer is yes, the control probably does not belong to the real security boundary.
A practical production model is therefore:
Model proposes → harness coordinates → runtime verifies → infrastructure executes
The higher layers can remain flexible. Teams can change models, prompts, planning algorithms, and agent frameworks without redesigning the foundational security policy every time.
That separation may become increasingly important as model capabilities improve.
A guardrail designed around what today’s agent is likely to attempt may become outdated when the next model discovers a new path. A correctly enforced filesystem or network boundary should continue to work regardless of how clever the model becomes.
What Comes After the Runtime?
The newest NVIDIA architecture points toward an additional step: moving some monitoring and enforcement outside the host itself.
In NVIDIA’s reference design, BlueField-4 sits on the communication path to the model and can provide out-of-band observability through Sentry. NVIDIA argues that separating this layer from the agent host makes it harder for a compromised workload to interfere with its own monitoring. NVIDIA Developer
Whether hardware-level agent monitoring becomes common remains an open question. It adds cost and architectural complexity, and many organizations will likely achieve sufficient controls through software runtimes, identity systems, API gateways, policy engines, and conventional infrastructure.
But the direction is worth watching.
AI security started largely with the question:
How do we make the model safer?
Agentic AI added another:
How do we control what the model can access?
The next question is now becoming:
Where should the system enforce those controls so the agent cannot bypass them?
That is why the runtime is starting to matter.
FAQ
What is AI agent runtime security?
AI agent runtime security refers to infrastructure-enforced controls that restrict what an AI agent can access or execute while it is running. These controls can include sandboxing, filesystem permissions, network policies, credential isolation, process restrictions, tool authorization, logging, and revocation.
How is runtime security different from AI guardrails?
Guardrails influence or evaluate model behavior. Runtime security enforces technical limits on the resulting actions. A guardrail may tell an agent not to access a resource; a runtime can make that resource inaccessible.
Does runtime security prevent prompt injection?
It does not necessarily stop prompt injection from influencing a model, but it can reduce the damage a successful injection can cause by restricting the files, credentials, tools, and network destinations available to the agent.
Is NVIDIA OpenShell required for AI agent runtime security?
No. OpenShell is one implementation of the secure-runtime concept. Similar principles can be implemented using sandboxing, container isolation, workload identity, policy engines, API gateways, network controls, and other security technologies.
Why is least privilege important for AI agents?
AI agents can dynamically decide which actions to take, sometimes based on untrusted context. Least privilege limits the maximum impact of a bad decision, compromised workflow, or manipulated instruction by restricting each agent to the resources and actions required for its task.
Final Thoughts
The most important change in agent security may not be a new model defense.
It may be deciding that the model should never be the final security authority in the first place.
Models and agent harnesses are good at reasoning through ambiguity. That is exactly why enterprises want to use them. But security boundaries need the opposite property: predictable decisions that remain enforceable even when the component inside the boundary behaves unexpectedly.
That makes the runtime an increasingly important layer.
The model can reason.
The agent can plan.
The runtime should still be able to say no.
And as AI agents gain access to more valuable systems, that “no” may matter more than another improvement in the model’s ability to behave correctly.